A Privacy Tools It supports financial institutions in complying with the LGPD (Brazilian General Data Protection Law) and the requirements of the Central Bank with consent governance, Open Finance, risk management, and evidence for audits.
Financial institutions process personal data on a large scale and under dual regulation: LGPD and the regulations of the Central Bank, the National Monetary Council (CMN), and the Superintendence of Private Insurance (SUSEP) regarding cybersecurity, outsourcing, and data sharing. Open Finance added customer consent as a central element of data sharing between institutions.
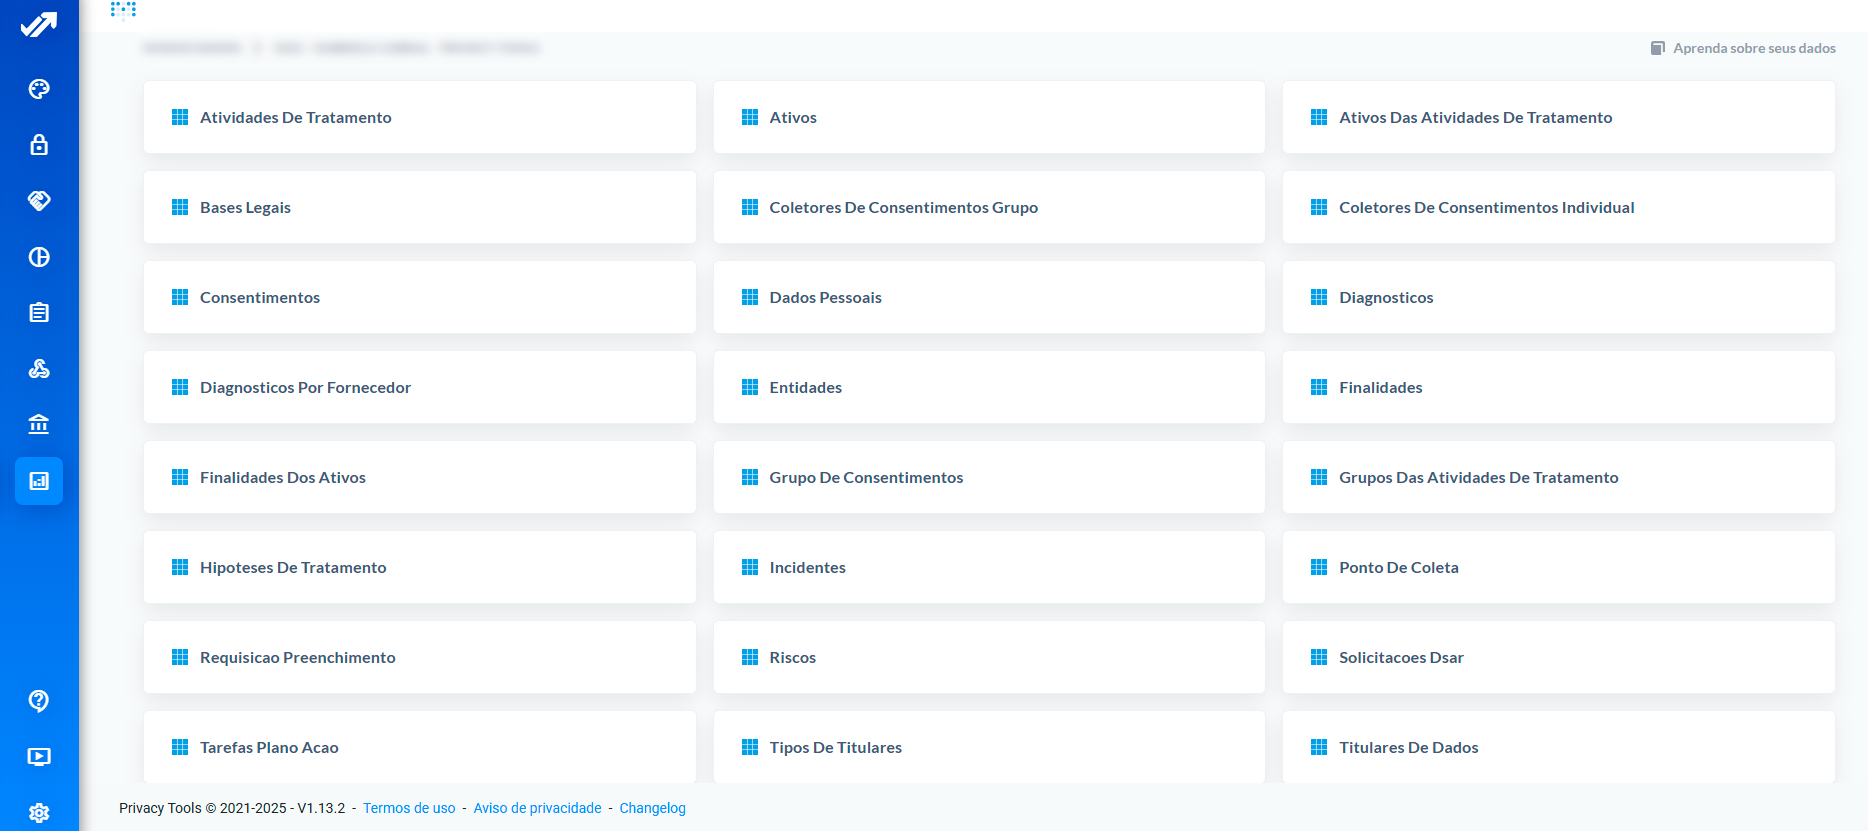
A Privacy Tools It brings together the mapping of processing activities, the management of consents integrated with Open Finance workflows, the support of data subjects, the management of risks and third parties, and audits in a complete environment, ready for the internal controls area.
Banks, cooperatives, insurance companies, fintechs, and administrators process personal data on a large scale and under dual regulation. LGPD It requires a legal basis for each processing activity (articles 7 and 11), allows processing for credit protection (article 7, X) and for fraud prevention in electronic systems (article 11, II, "g"), guarantees the client the review of automated credit and profile decisions (article 20), and requires a governance program (article 50). The Central Bank and the National Monetary Council (CMN), in turn, impose a cybersecurity policy and rules for contracting relevant cloud services (CMN Resolution 4.893/2021), and Open Finance (Joint Resolution No. 1/2020) depends on specific, revocable consent with a time limit. SUSEP applies equivalent rules to insurance companies, and the Banking Secrecy Law (LC 105/2001) remains in effect.
Open Finance consent without due diligence; profiles and scores without explanation to the client; client data in spreadsheets and emails from agencies; correspondents and debt collectors with access beyond what is necessary; cloud contracted without the evaluation required by the regulator; and service channels used by fraudsters to obtain third-party data.
O RCI Bank BrazilThe financial arm of the Renault-Nissan-Mitsubishi alliance manages Open Banking consents with the Privacy Tools. O Banese It manages the data of 800 data subjects across 63 branches using cookies, policies, data mapping, and data discovery. Sicoob Central Crediminas imported 16 processes and integrated 1.500 users via API for 73 cooperatives, and the Sancor Insurance conducted its compliance program with the platform.
Yes. Consent Management records the purpose, duration, channel, and revocation of each consent and integrates via API with the institution's systems, as Banco RCI Brasil does.
Inventorying the models in AI Governance, documenting criteria and controls, and ensuring a human review workflow when requested by the client, through the DSAR module.
With applicant authentication in the DSAR module: email confirmation and validation before any release, with a record of who accessed what.
The platform is SaaS and Data Discovery can be installed on-premise. The cloud provider assessment required by the regulator is conducted within the Third-Party Risk Management framework, using questionnaires, scoring, and an action plan.
The program can be centralized at the central cooperative and distributed to individual cooperatives, with activities, responsible parties, and indicators for each entity, as is the case with Sicoob Central Crediminas.
Request a demo from our team and see the platform in the context of your financial institution.